Limit Admin Access for Better IT Security
IT Security, Employee Access, Administrator Rights
Why Your Employees Shouldn’t Have Administrator Access to Their Computers
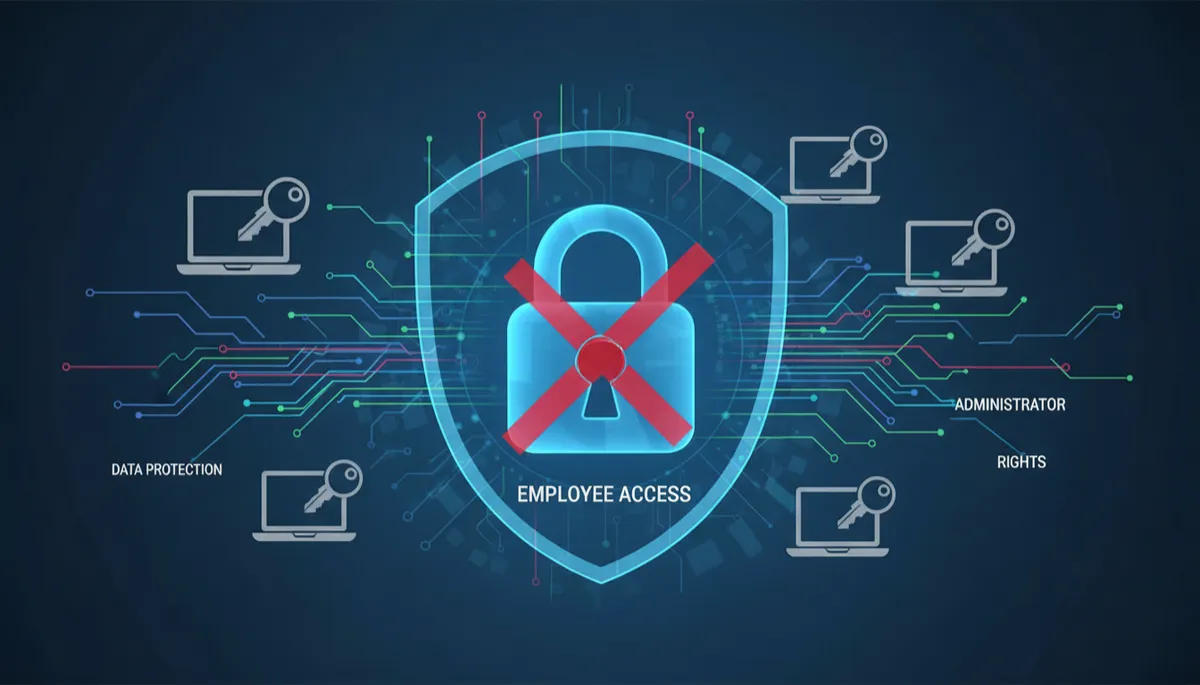
For modern businesses and agencies, tightening Employee Access is no longer optional. Allowing staff full Administrator Rights on their devices can quietly undermine Computer Security, Data Protection, and effective IT Management across your organization.
The Hidden Risk of Administrator Rights
When employees have unrestricted Administrator Access, they can install any software, change security settings, and bypass corporate policies. Even well‑intentioned staff may unknowingly introduce malware, shadow IT tools, or misconfigurations that weaken Computer Security and expose sensitive data.
From an IT Management perspective, standardizing Access Control is essential. Centralized control allows your IT team—and partners like All -N- One Tech Solutions—to patch systems consistently, enforce encryption, and monitor endpoints for suspicious activity. This discipline directly supports stronger Data Protection and regulatory compliance.
Reduce attack surface by limiting unnecessary Employee Access
Ensure only approved, secure applications are installed
Simplify audits and incident response for your IT team
Centralized access control dramatically lowers the chance of costly security incidents.
The solution is a least‑privilege model: grant employees only the access they need, while reserving Administrator Rights for IT professionals. With the right policies, tooling, and support, you protect your business, maintain productivity, and keep every device aligned with your security strategy.